Fault Injection Attacks (FIA)
This is a grad-level introduction to Fault Injection Attacks (FIA). The main target audience is grad students from CS and ECE, e.g., CS grads with some knowledge about security in general but looking to expand their security knowledge to hardware, and ECE grads with knowledge of digital circuits and VLSI but wondering what hardware security, especially fault injection, looks like. After taking this course, students should have a better understanding of the difference and connection between software security and hardware security, and major topics in fault injection, including both research and applied techniques. Undergrads are welcome to audit this course with permission from the instructor.
Prerequisite (ideal but not mandatory):
- General knowledge of computer security
- General knowledge of digital circuits
- General knowledge of computer architecture
- General knowledge of hardware security
Syllabus:
- Intro
- SoK: A Beginner-Friendly Introduction to Fault Injection Attacks
- The Sorcerer’s Apprentice Guide to Fault Attacks
- Rowhammer Attacks
- Flipping Bits in Memory Without Accessing Them: An experimental Study of DRAM Disturbance Errors
- Drammer: Deterministic Rowhammer Attacks on Mobile Platforms
- Flip Feng Shui: Hammering a Needle in the Software Stack
- Throwhammer: Rowhammer Attacks over the Network and Defenses
- TRRespass: Exploiting the Many Sides of Target Row Refresh
- ZENHAMMER: Rowhammer Attacks on AMD Zen-based Platforms
- ECC.fail: Mounting Rowhammer Attacks on DDR4 Servers
- Phoenix: Rowhammer Attacks on DDR5 with Self-Correcting Synchronization
- GPUHammer: Rowhammer Attacks on GPU Memories are Practical
- GPUBreach: Privilege Escalation Attacks on GPUs using Rowhammer
- GeForge: Hammering GDDR Memory to Forge GPU Page Tables for Fun and Profit
- GDDRHammer: Greatly Disturbing DRAM Rows — Cross-Component Rowhammer Attacks from Modern GPUs
- GPUThor: Amplifying Rowhammer Attacks via Non-Uniform Patterns to Exploit ECC-Protected GPUs
- From Lab to Fleet: Building and Developing a Practical Rowhammer Defense in Cloud SoCs
- Voltage/Clock Glitching
- An In-depth and Black-box Characteraization of the Effects of Clock Glitches on 8-bit MCUs
- Fault Injection using Crowbars on Embedded Systems
- Controlling PC on ARM using Fault Injection
- CLKScrew: Exposing the Perils of Security-Oblivious Energy Management
- VoltJockey: Breaching TrustZone by Software-Controlled Voltage Manipulation over Multi-core Frequencies
- Plundervolt: Software-based Fault Injection Attacks against Intel SGX
- V0LTpwn: Attacking x86 Processor Integrity from Software
- VoltPillager: Hardware-based Fault Injection Attacks against Intel SGX Enclaves using the SVID Voltage Scaling Interface
- One Glitch to Rule Them All: Fault Injection Attacks Against AMD’s Secure Encrypted Virtualization
- Minefield: A Software-only Protection for SGX Enclaves against DVFS Attacks
- Oops..! I Glitched It Again! How to Multi-Glitch the Glitching-Protections on ARM TrustZone-M
- Chypnosis: Undervolting-based Static Side-channel Attacks
- Electromagnatic Fault Injections (EMFI)
- Magnetic Microprobe Design for EM Fault Attack
- ElectroMagnetic Fault Injection in Practice
- Electromagnetic Fault Injection: The Curse of Flip-flops
- Electromagnetic Fault Injection: How Faults Occur
- New Probe Design for Hardware Characterization by ElectroMagnetic Fault Injection
- Inducing Local Timing Fault through EM Injection
- BADFET: Defeating Modern Secure Boot Using Second-Order Pulsed Electromagnetic Fault Injection
- MIN()imum Failure: EMFI Attacks against USB Stacks
- SiliconToaster: A Cheap and Programmable EM Injector for Extracting Secrets
- Design Considerations for EM Pulse Fault Injection
- BAM BAM!! On Reliability of EMFI for in-situ Automotive ECU Attacks
- Breaking Espressif’s ESP32 V3
- Laser Fault Injection (LFI)
- Optical Fault Induction Attacks
- LLFI: Lateral Laser Fault Injection Attack
- Injecting Permanent Faults into the Flash Memory of a Microcontroller with Laser Illumination During Read Operations
- Basilisk: Remote Code Execution by Laser Excitation of P-N Junctions without Insider Assistance
- Security through Transparency: Tales from the RP2350 Hacking Challenge
- Body Biasing Injection (BBI)
- Techniques for EM Fault Injection: Equipments and Experimental Results
- Yet Another Fault Injection Technique: by Forward Body Biasing Injection
- Voltage Spikes on the Substrate to Obtain Timing Faults
- Body Biasing Injection Attacks in Practice
- Low-Cost Body Biasing Injection (BBI) Attacks on WLCSP Devices
- Acoustic Fault Injection
- Rocking Drones with Intentional Sound Noise on Gyroscopic Sensors
- Injected and Delivered: Fabricating Implicit Control over Actuation Systems by Spoofing Inertial Sensors
- Un-Rocking Drones: Foundations of Acoustic Injection Attacks and Recovery Thereof
- AquaSonic: Acoustic Manipulation of Underwater Data Center Operations and Resource Management
- TimeTravel: Real-time Timing Drift Attack on System Time Using Acoustic Waves
- Banshee: Target Switch Attacks on Gimbal-Stabilized Visual Tracking Systems via Acoustic Injection
- FPGA
- The Unpatchable Silicon: A Full Break of the Bitstream Encryption of Xilinx 7-Series FPGAs
- Deep-Dup: An Adversarial Weight Duplication Attack Framework to Crush Deep Neural Network in Multi-Tenant FPGA
- DeepShuffle: A Lightweight Defense Framework against Adversarial Fault Injection Attacks on Deep Neural Networks in Multi-Tenant Cloud-FPGA
- Faults that Persist: Fault-Injection Attacks and ASCON-Based Defense in Multi-Tenant FPGAs
Lab Assignments:
- Rowhammer on DDR3
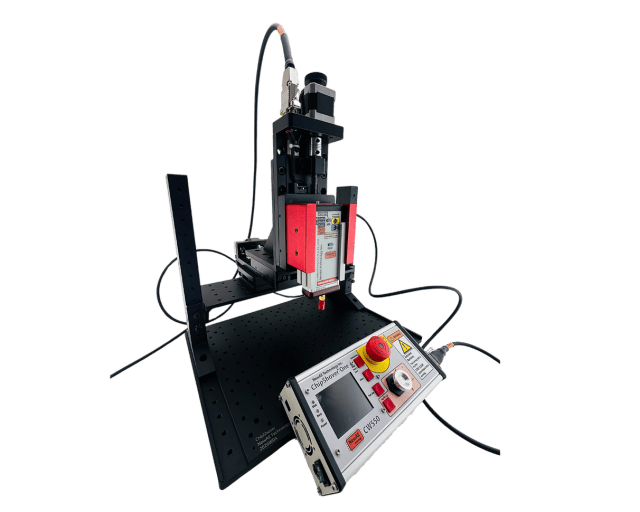
- Voltage glitching using ChipWhispereNano
- EMFI probe design